Business · Cybersecurity · France
A French cooperative bank with 5.8 million customers says attackers came in through a third-party service provider, used an account belonging to the bank itself to fire fraudulent transfers at other banks, and left about €100 million missing. A blockchain investigator says the real total — run out through crypto exchanges — is higher. The bank confirms the order of magnitude, and nothing more.
Track it live: Crypto market tracker
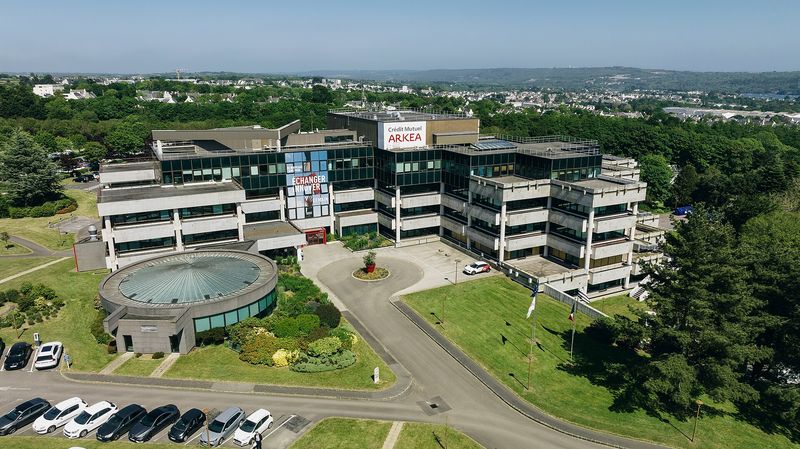
LE RELECQ-KERHUON, France, November 5, 2026 — The Credit Mutuel Arkea cyberattack is, by the bank’s own provisional count, a €100 million theft: on Thursday the French cooperative banking group said about €100 million ($112.61 million) was missing after attackers entered its systems through a third-party service provider’s platform and used an account belonging to the bank itself to make fraudulent transfers to other banks. Some of the money has been blocked, recovery work is under way, and the bank says it cannot yet say how much will ultimately be recovered. Customer accounts were not affected, the group stressed, and the loss — set against €211.5 billion in assets and more than 5.8 million customers — does not threaten its financial health.
What makes the case larger than one bank’s bad week is the second set of numbers attached to it, and the dispute over which of them is real. Blockchain investigator ZachXBT, who identified Arkéa as the victim before the bank had confirmed anything beyond an incident, estimates that more than $133 million (about €118 million) left through accounts at cryptocurrency exchanges. The bank said it does “not confirm” that figure and can “only validate the order of magnitude.” A third figure, from blockchain analytics firm Bitquery, traces about $108.8 million in the USDC stablecoin moving out of OKX, Kraken and Crypto.com to 15 wallets over 21 hours on November 1–2. Three numbers, three owners, three different scopes — this article keeps them separate throughout, because merging them would produce a total that nobody has actually claimed. The crypto getaway leg, it should be said plainly, is ZachXBT’s account of where the money went; the bank has confirmed fraudulent transfers to other banks, not a conversion into cryptocurrency. And no attribution for the attack has been announced by anyone.
What the bank says happened
Crédit Mutuel Arkéa is the Brittany-based arm of the wider Crédit Mutuel group: a cooperative banking and insurance group headquartered at Le Relecq-Kerhuon, outside Brest, with more than 5.8 million customers, €211.5 billion in assets, and subsidiaries that include Fortuneo, one of France’s best-known online banks. According to the bank’s statements, the attackers did not break down its own front door. They came in through the platform of a third-party service provider — a vendor the bank has declined to identify — and from there were able to operate an account belonging to the bank itself, sending fraudulent transfers out to other banks. The significance of that route is easy to miss: transfers sent from the bank’s own account, through channels the bank itself uses, look to receiving institutions like ordinary interbank business, which is one reason sums of this size can move before alarms trip.
The bank has been specific about two things the attack was not. It explicitly rejected reports that Fortuneo was the entry point, and it denied that internal human error caused the breach. It has also repeated, in every statement, that the money taken was the bank’s own: customer accounts were not touched, and no customer’s assets were affected. As a precaution the bank temporarily suspended some transactions, which delayed some customer transfers; most operations had resumed by Wednesday, November 4, the day the attack was made public. The bank said it informed the European Central Bank, French banking supervisors and prosecutors, and the Paris prosecutor’s office said its cybercrime unit received the bank’s complaint on Wednesday and immediately opened an investigation into an organised attack on an automated data-processing system — the French legal framing for a coordinated intrusion into a computer system.
Timeline: from quiet outflows to a public heist
November 1–2. Over roughly 21 hours, about $108.8 million in USDC is withdrawn from accounts at three crypto exchanges — OKX, Kraken and Crypto.com — to 15 wallets, according to Bitquery’s later tracing. At the time, nothing public connects these flows to any bank; on the blockchain they are simply very large stablecoin withdrawals.
November 2. ZachXBT, a pseudonymous investigator who tracks stolen funds on public blockchains, flags suspected losses of more than $106 million from exchange accounts belonging to an unnamed European entity. He does not yet name the victim.
November 3. ZachXBT reports finding a further $27 million in withdrawals, raising his estimate to more than $133 million, and says the total could grow once over-the-counter trades are counted.
November 4. ZachXBT names Crédit Mutuel Arkéa as the suspected victim. The bank confirms a cyberattack involving fraudulent transactions, says the incident is contained, and begins gradually resuming operations; some transfers had been delayed by precautionary suspensions. It tells reporters its losses are lower than the $133 million figure reported by CoinDesk, describes the amount as not of a nature to undermine the group’s financial strength, and says a final figure would be premature. The Paris prosecutor’s cybercrime unit opens its investigation.
November 5. The bank puts its provisional number on the record: about €100 million missing, some funds blocked, recovery under way, and no estimate yet of how much will be recovered. Asked about the €118 million figure, it says it does not confirm it and can only validate the order of magnitude.
Three numbers, three different stories
€100 million — the bank’s provisional figure
The €100 million ($112.61 million) is the only number that comes from the institution that lost the money, and the bank itself labels it provisional. It is, in effect, the bank’s current internal accounting of what left and has not come back: transfers identified as fraudulent, minus what has already been blocked or recovered, at a moment when the bank concedes the work is unfinished. Provisional figures in bank heists move in both directions — down as freezes bite and recalls land, up as investigators find transfers nobody had flagged. What the bank has not done is publish a final loss, a schedule for one, or any breakdown of where the transfers went.
More than $133 million — ZachXBT’s estimate, unconfirmed
ZachXBT’s figure — more than $133 million, about €118 million — is built from the other end: not from the bank’s books but from the blockchain, by watching money leave exchange accounts he associates with the victim. He built it in stages, from more than $106 million on November 2 to more than $133 million on November 3, and he has said it could rise further once over-the-counter trades, which leave no public trail, are counted. It is an estimate by an outside investigator, however experienced, and the bank’s response to it was carefully limited: it does “not confirm” the figure and can “only validate the order of magnitude.” That formulation neither endorses $133 million nor rules it out — it concedes that the theft was of that rough size while reserving the exact number. Readers should hold it as what it is: the largest claimed figure, publicly sourced to one investigator’s analysis, not bank-confirmed.
$108.8 million — what Bitquery could actually trace
Bitquery’s $108.8 million is the narrowest of the three, and deliberately so: it counts only what the firm could trace on-chain — USDC withdrawn from OKX, Kraken and Crypto.com to 15 wallets over 21 hours on November 1–2. It cannot see the bank transfers that preceded any crypto conversion, cannot see inside exchange accounts, and does not claim to measure the bank’s total loss. Its value is different from the other two figures: it is the only one that is independently checkable against public blockchain records, and it establishes at minimum that nine figures’ worth of stablecoin moved out of three major exchanges, to a small set of fresh wallets, in under a day, in the same window the bank was being robbed. Whether every dollar of it is Arkéa’s money is inference; that the flows happened is record.
Why this matters
The vendor is the vault door now
The single most consequential detail in the bank’s account is the route in: not a smashed password at the bank, but a third-party service provider’s platform. Modern banks run on vendors — payment processors, account-servicing platforms, connectivity providers, screening and reconciliation tools — and each integration is a set of credentials and permissions that reach inside the bank’s own operations. An attacker who compromises the right vendor does not need to defeat the bank’s defences at all; they arrive carrying the vendor’s trusted access, and in this case, according to the bank, were able to operate an account belonging to the bank itself. Supervisors in Europe have spent several years warning about exactly this concentration and contagion risk, and the Arkéa case will be cited in that argument for years: the question it poses to every large bank is not “are your walls strong?” but “do you actually know whose keys open them?”
Fiat in, crypto out, at machine speed
The second lesson is about the getaway. Bank transfers, once sent, move through a system built on trust between institutions, with recalls that depend on the receiving bank’s cooperation and speed. Cryptocurrency — on ZachXBT’s account of this heist, which the bank has not confirmed — removes the cooperation requirement almost entirely: funds converted into a stablecoin like USDC and withdrawn to self-controlled wallets can be swapped, split and moved across chains in minutes, at any hour, on a Sunday night. Bitquery’s trace, if the flows are indeed the bank’s money, shows the shape of it: 21 hours, three exchanges, 15 wallets, $108.8 million. The defensive counterweight is narrow and time-limited: while stolen value still sits at a regulated exchange, or in a centrally issued stablecoin, it can sometimes be frozen — Crypto.com told CoinDesk it had taken action to block funds linked to the incident, and OKX said it had spotted unusual activity on an institutional customer’s account and frozen it. Once value is swapped into assets no issuer can freeze and moved beyond cooperative venues, that window closes. Recovery in cases like this is therefore a race measured in hours, run simultaneously by bank security teams, exchange compliance desks and police — against an opponent who only has to win it once.
Successful heists on big regulated banks are rare — which is the point
Reuters described the incident as a rare successful heist against a large financial institution, and the rarity is worth dwelling on. Large regulated banks are breached constantly and robbed at this scale almost never, because the controls that matter for theft are different from the controls that matter for data: moving nine figures out of a bank requires defeating transaction monitoring, payment limits, counterparty checks and human review, then surviving the recall machinery of the interbank system. When a theft of this size succeeds, investigators therefore start from the assumption that something structural failed — an access path that bypassed the normal gauntlet, such as a trusted vendor channel or the bank’s own operating account. That is why the vendor route, and the bank’s insistence that neither Fortuneo nor internal human error was to blame, are the details investigators and supervisors will press on: the answer determines whether this was one bank’s misfortune or a diagram of a weakness shared by every institution using similar providers.
The loss in context: €100 million against €211.5 billion
Set against the group’s balance sheet, the provisional loss is small: €100 million is roughly 0.05 percent of €211.5 billion in assets — about five cents in every hundred euros the group holds. That arithmetic is the substance behind the bank’s statement that the loss does not threaten its financial health, and it is why the story is a security story rather than a solvency story. For the group’s more than 5.8 million customers, the practical impact was narrower still: no customer money was taken, and the visible cost was delay — transfers held up while some transactions were suspended as a precaution, with most operations resumed by November 4. The real costs sit elsewhere and arrive later: the unrecovered residue of the theft, whatever it proves to be; the investigation and remediation bill; potential supervisory consequences if the vendor oversight is judged deficient; and the reputational cost of having been named, by an outside investigator, before its own disclosure had caught up with events.
Who benefits, who loses — and what the regulators are doing
The beneficiaries, beyond the thieves themselves, are few and mostly incidental: rival banks will quietly market their own security postures; security vendors will sell the post-mortem; and investigators like ZachXBT gain standing each time an institution’s eventual disclosure lands near an estimate he published first. The losers are clearer. The bank absorbs the loss and the scrutiny. Its unnamed service provider faces the most dangerous question in the case — how its platform became a door into a bank’s own account — with contractual, regulatory and commercial consequences that will follow whatever investigators conclude. The exchanges in the traced flows face their own examination of how institutional accounts could be drained at that speed, even as two of them say their interventions blocked part of the money. And every other bank using comparable vendor arrangements loses the comfort of assuming the arrangement was safe because it was common.
Regulators and prosecutors are already inside the story. The bank says the ECB and French banking supervisors were informed — the ECB supervises significant euro-area institutions and treats major cyber incidents as supervisory events, which means Arkéa can expect its vendor-risk management, incident detection and disclosure timeline to be examined, not just the theft. The Paris prosecutor’s cybercrime unit is running the criminal side, an investigation into an organised attack on an automated data-processing system. Critics of the bank, and of the sector, make three arguments worth recording as arguments: that disclosure lagged the money — the traced outflows began November 1, public confirmation came November 3–4, and the bank’s own figure arrived November 5; that outsourcing core functions without bank-grade control over the vendor’s security is a governance failure, not bad luck; and that a system in which a pseudonymous investigator can see a bank being robbed on a public ledger before the bank announces it has its transparency backwards. The bank’s defenders can answer each in part: detection and containment inside days is not slow by industry standards, the figure gap reflects a genuine fog in the first week of a heist, and the bank did confirm the order of magnitude rather than hiding behind a denial. Both readings are now in the hands of supervisors who can compel the underlying facts.
Background: the third shock in a bruising week for digital money
The Arkéa heist did not happen in isolation, and the week around it explains the speed of the official reaction. It follows last week’s theft of $6.3 billion in cryptocurrency from the Binance exchange — the largest crypto theft ever recorded, which the FBI has blamed on North Korea — and a wave of cyberattacks on internet-connected refrigeration systems in Europe, including the attack that turned French supermarket freezers into ovens across some 300 stores. Neither earlier incident is evidence about who attacked Arkéa, and no official has linked them; ZachXBT has said he has a high degree of confidence this theft is not the work of North Korea’s Lazarus operation, but that is an investigator’s assessment, not an attribution, and none has been announced. What the sequence does establish is the environment: in the space of a fortnight, attackers have hit a crypto exchange for billions, industrial control systems in European supermarkets, and a top-tier cooperative bank for nine figures — three different targets, three different techniques, one shared feature, which is that the defences each victim trusted were routed around rather than broken through.
Arkéa itself is an unlikely target in one respect and an obvious one in another. As a cooperative group rooted in Brittany and the South-West, owned by its members rather than traded on a stock exchange, it has historically kept a lower profile than France’s listed banking giants. But it is large — €211.5 billion in assets puts it among Europe’s significant institutions — it runs a major online bank in Fortuneo, and like every modern bank it is stitched into the same vendor and payments infrastructure as its peers. Heists of this kind are not chosen for the victim’s fame; they are chosen for the victim’s plumbing.
What happens next
The recovery race comes first, and it is already partly run. The bank says some funds have been blocked; the open question is how the blocked share compares with the total once the accounting settles. Freezes work where the money still touches a cooperative institution — a receiving bank that can be persuaded or ordered to hold a transfer, an exchange that can lock an account, a stablecoin issuer that can blacklist an address. Each hop the money has already made through uncooperative venues shrinks the recoverable share, which is why the final loss figure, when the bank publishes one, will say as much about the getaway’s speed as about the theft’s size. Expect the provisional €100 million to be revised, and expect the direction of the revision to be fought over by everyone who has published a number.
The investigation runs on a longer clock. The Paris prosecutor’s cybercrime unit must reconstruct how the vendor platform was entered, how the bank’s account was operated, and where the transfers were instructed to go — work that depends on logs and records held by the provider, the bank, receiving banks and exchanges in several jurisdictions. Attribution, if it comes, will come from that process or not at all; until then, every named suspect in public discussion is speculation, and this article treats it as such. On the supervisory track, the ECB and French authorities will want the bank’s incident timeline, its vendor contracts and its detection story; outcomes range from quiet remediation demands to public enforcement, and European supervisors have used cases like this before to tighten third-party risk expectations across the whole sector, not just at the victim.
Disclosure is the third front. The bank has promised, in effect, a final figure when its teams finish assessing the damage; whether that figure vindicates its €100 million, drifts toward ZachXBT’s $133 million, or lands somewhere neither camp predicted, it will be the number the lawsuits, the supervisors and the history books use. The identity of the service provider is the other withheld fact with a fuse on it: it will surface in court filings, supervisory action or the provider’s own disclosures, and when it does, every bank that shares the vendor will have to answer the same questions Arkéa is answering now. Until those two facts land, the honest summary of the Credit Mutuel Arkea cyberattack is the one the evidence supports: a very large bank, entered through a partner’s door, robbed through its own account, missing a provisional €100 million — and a public argument about the true total that the blockchain started and only the bank’s final accounting can end.
Related coverage: FBI blames North Korea for the $6.3 billion Binance hack and hackers turned French supermarket freezers into ovens in the Danfoss cyberattack.
Sources
Reuters, November 5, 2026, “French bank Credit Mutuel Arkea says €100 million missing after cyberattack” — the bank’s provisional €100 million ($112.61 million) figure, funds blocked and recovery under way, the third-party provider route and the bank’s own account, customer accounts unaffected, the Fortuneo and human-error denials, the ECB and French supervisors informed, the Paris prosecutor’s investigation, and the group’s 5.8 million customers and €211.5 billion in assets.
Reuters, November 4, 2026, reporting on the bank’s initial confirmation — losses lower than the $133 million reported by CoinDesk, the amount described as not of a nature to undermine the group’s financial strength and soundness, some transfers delayed by precautionary suspensions, and the attack characterised as a rare successful heist against a large financial institution, following the Binance theft and the European refrigeration-system attacks.
Agence France-Presse (AFP), November 4–5, 2026 — the Paris prosecutor’s cybercrime unit’s investigation into an organised attack on an automated data-processing system, opened on the bank’s complaint, and the bank’s provisional estimate as carried in French reporting.
CoinDesk, November 4, 2026, “ZachXBT names French bank Crédit Mutuel Arkéa in $133M crypto exchange theft” — ZachXBT’s identification of the bank and his estimate of more than $133 million, Bitquery’s tracing of about $108.8 million in USDC from OKX, Kraken and Crypto.com to 15 wallets over 21 hours on November 1–2, the bank’s confirmation of the attack to CoinDesk, and Crypto.com’s and OKX’s statements that they blocked funds and froze accounts linked to the incident.
Crédit Mutuel Arkéa, public statements, November 4–5, 2026 — the bank’s account of entry through a third-party service provider’s platform, fraudulent transfers made from an account belonging to the bank, the rejection of Fortuneo as the entry point, the denial of internal human error, the statement that it does “not confirm” the €118 million figure and can “only validate the order of magnitude,” and its position that the loss does not threaten the group’s financial health.